

Github Pwang00 Cryptographic-attacks: Repository Containing Implementation Of Assaults On Modern Public Key Cryptosystems And Symmetric Key Ciphers Github
Accordingly, it’s important to detect such an attack and then limit it to be assured that the harm triggered might be minimized. Lapses in any of those practices open the door to key leakage or misuse, usually enabling attackers to decrypt or forge delicate knowledge while not having to interrupt the underlying encryption itself. Organizations should acknowledge that cryptographic energy degrades over time as extra research uncovers weaknesses and as computational power will increase. With Out a deliberate strategy to evaluation and update cryptographic algorithms in deployed systems, what was as soon as “secure” can become obsolete. Menace modeling should embrace cryptographic assets, contemplating potential attackers, abuse circumstances, and failure modes associated to cryptography.
Broken Password Hashing And Credential Leaks
The majority of extensively used encryption techniques, according to the Kerckhoff method, use identified, non-secret cryptographic procedures. Safety weaknesses frequently emerge from outdated cryptographic libraries, misused APIs, or insecure third-party parts. Adopting a policy of regular updates, immediate patching, and close monitoring of modifications in cryptographic dependencies is important to forestall publicity to identified vulnerabilities. Instruments like software composition analysis and automated dependency monitoring help determine and report issues before they are exploitable. Damaged password hashing happens when systems use fast or outdated hash features that weren’t designed to withstand offline assaults.
- By standardizing TLS variations and cipher suite settings on the edge, Alteon helps prevent insecure downgrade situations and reduces exposure to inconsistent encryption throughout backend providers.
- Once encryption is weakened or bypassed, visitors confidentiality and integrity can not be assumed.
- It has keys for encryption (transforming plaintext into unreadable ciphertext) and decryption (reverting ciphertext back to readable form).
- Periodic critiques by impartial specialists or penetration testers who specialize in cryptographic techniques provide an external perspective and often catch issues missed by inner groups.
- I plan to complete all current public key attacks sooner or later and significantly broaden attack support for symmetric key primitives, as the latter has been comparatively lacking for the past few years.
Stopping Cryptographic Attacks
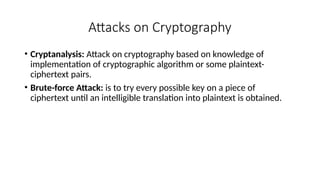
Algorithms similar to MD5 or unsalted SHA-1 enable attackers to test massive numbers of candidate passwords rapidly as soon as a hash database is obtained. The failure just isn’t in the breach itself, but within the lack of ability of the hashing design to slow or forestall password restoration after exposure. Repository containing implementation of assaults on modern public key cryptosystems and symmetric key ciphers. Hence, whereas attacking an encryption algorithm, the adversary often has two primary goals, searching for the key code or discovering the open text that meets the encryption code. A strong system additionally attempts to identify proof of malicious exercise and prohibit the effect of any assaults.

Consequences Of Cryptographic Failures
Periodic critiques by impartial specialists or penetration testers who specialize in cryptographic techniques provide an external perspective and infrequently catch issues missed by internal groups. Committing to a schedule of periodic evaluation retains cryptographic controls present and tuned to the evolving threat landscape. Incorrect use of APIs, misunderstanding menace fashions, skipping very important steps like verification of cryptographic parameters, or custom-building cryptographic modules with out deep expertise create numerous failure factors. This also includes logic flaws similar to misuse of encryption modes, hardcoded IVs (initialization vectors), or insecure random quantity generation.
Wi-fi Community Safety
These services also can assist “virtual patching” when cryptographic libraries or software https://usamars.com/development-of-american-high-technologies-and-features.html elements require urgent remediation. To enhance detection and response, Cloud Community Analytics offers traffic visibility and anomaly detection that can assist identify suspicious patterns in preserving with downgrade attempts, MITM probing, or credential abuse. Together, these capabilities assist organizations enforce stronger encryption practices and cut back the likelihood that cryptographic weaknesses will turn into exploitable security gaps. Cryptographic failures often stem from weak configurations, outdated protocols, insecure information dealing with, or inconsistent enforcement across advanced environments.
Jeremie holds a Master’s diploma in Telecommunications, and has an abiding ardour for technology and a deep understanding of the cybersecurity business. Jeremie thrives on human exchanges and strives for excellence in a multicultural surroundings to create innovative cybersecurity solutions. As of now, I truly have written up a summary of the first few chapters of Craig Costello’s Pairings for Newbies and a SageMath script demonstrating elliptic curve point addition and doubling in projective coordinates. In an MITM attack, a hacker intercepts and potentially alters communication between two events. If you are the writer of this paper and no longer wish to have it revealed on StudyCorgi, request the removal.
Algorithms which have withstood significant public scrutiny and evaluation present one of the best assurance against future assaults, as opposed to proprietary or outdated ciphers. Avoiding deprecated or experimental algorithms is crucial to sustaining the integrity of protected information. TLS failures often stem from configuration choices quite than broken cryptographic algorithms. Allowing obsolete protocol variations or weak cipher suites gives attackers room to interfere with connection negotiation. As Quickly As encryption is weakened or bypassed, visitors confidentiality and integrity can no longer be assumed. Misconfiguration of cryptographic settings can easily undermine otherwise strong safety controls.


