

Uncategorized
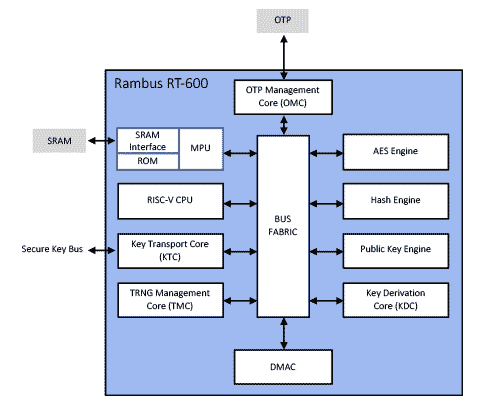
Safe Boot is binary — the firmware both passes verification or it doesn’t. Measured Boot creates a detailed log of every part that loaded, allowing a remote verifier to evaluate the exact configuration of the system. The Boot ROM should be mask ROM — written throughout chip fabrication and physically unimaginable to switch.
Person Will Get A New Device And Is Attempting To Log Right Into A Cell App Using 2fa
As threats evolve — from quantum computing to AI-powered fault injection — this foundation must evolve with them. The design choices made in silicon right now will determine the safety posture of billions of gadgets for the next decade. When a SoC powers on, the processor begins executing from a set address that points into the Boot ROM. This ROM incorporates the first-stage boot code and the public key (or hash of the basic public key) used to verify the subsequent stage.
How Miniorange Helps To Mitigate Rot Attacks?
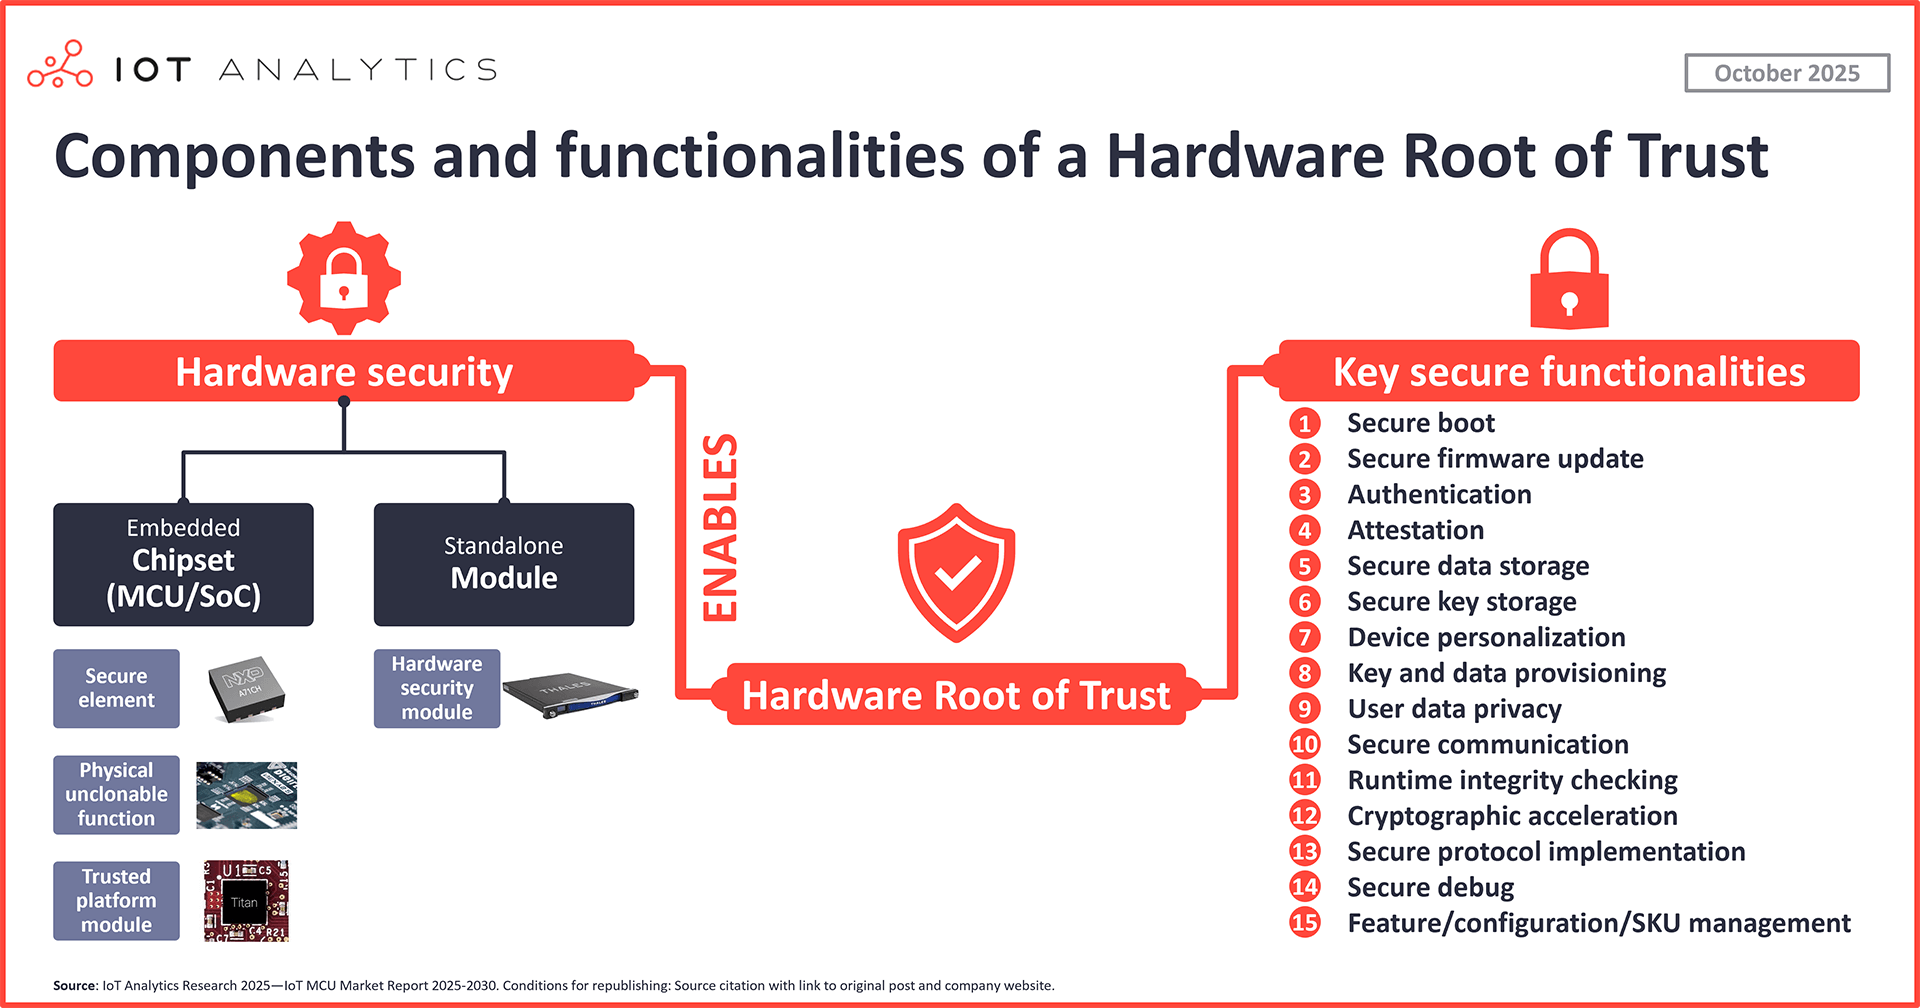
Of course, the system could be booting successfully, but what occurs if some piece of malware is the very first thing that runs, and the rest of the software program is trusting that code? A Root-of-Trust ensures from the moment the reset vector is executed that we are running the right software. Taking the common components from the previous section’s definitions of a root of belief, we will distill the basic elements of a RoT into the above listing. The first merchandise is “trust” – that is, the system can rely upon the RoT at all times, especially at boot up. Since there isn’t a way to independently confirm the authenticity of a RoT at boot up, then it must be implicitly trusted proper at power/start up of a system. To accomplish that, it is strongly recommended that before set up of a RoT, that it is verified to be legitimate and genuine, and that a document of that verification is stored on the RoT itself, in order that it could be re-verified throughout runtime, as needed.
Physical Tampering Assaults
Plan alternative when hardware, firmware, algorithms, possession, or trust coverage adjustments. Adopting miniOrange’s IAM options means shifting to a layered defense system and constructing a resilient foundation towards probably the most subtle cyber dangers, together with Root of Belief assaults. A firmware attack targets the firmware of a device, which is a software that tells the device (computer, smartwatch, or smartphone) how to function when powered on.
Roots Of Trust Rot
- An invasive assault may take the form of fault injection, or decapping and reverse engineering the RoT.
- A root can prove identification or measured state with out proving bodily location, present behavior, absence of malware after measurement, or protected utility logic.
- Once the system has booted securely, certain operations want ongoing safety throughout runtime — cryptographic key operations, biometric processing, DRM, secure funds.
- There isn’t any different component that can verify/authorize/attest to the validity of the RoT – it’s element zero of the system.
- Provide chain attacks exploit the vulnerabilities of an organization, which could embrace inner or exterior vulnerabilities such as software, hardware, or business operations.
Once within the microcontroller, we do not want this data to be changeable. Once the system has booted securely, sure operations need ongoing safety during runtime — cryptographic key operations, biometric processing, DRM, safe payments. A TEE is an execution setting https://www.discoveryon.info/category/business/ isolated from software program outdoors the TEE.